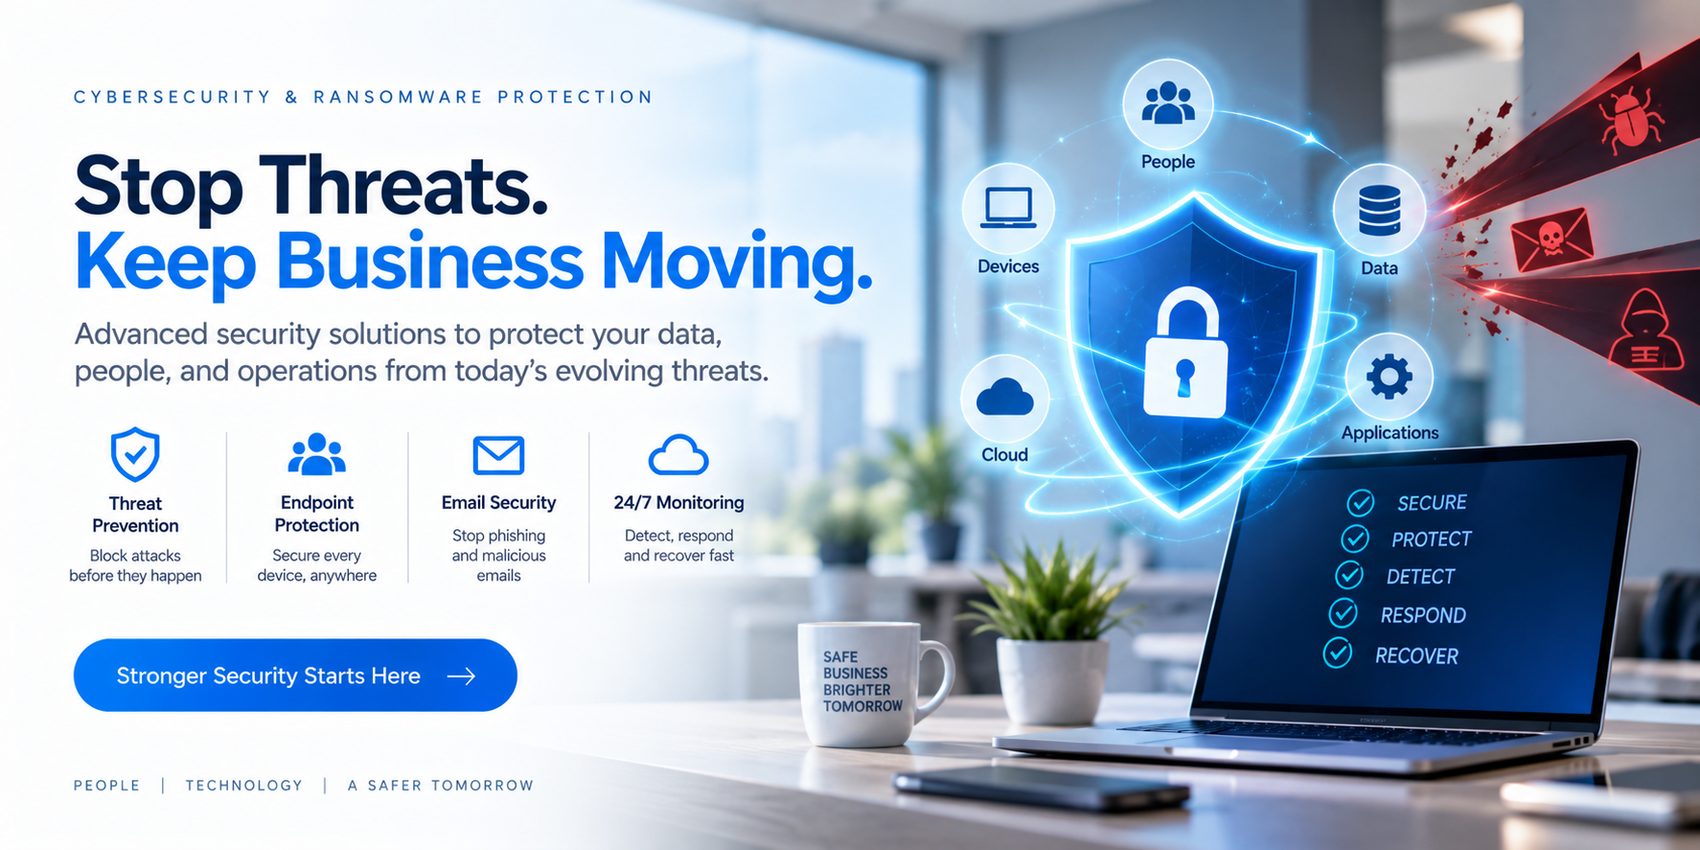
Stop Threats. Keep Business Moving.
Advanced security solutions to protect your data, people and operations from today's evolving threats.
- Secure
- Protect
- Detect
- Respond
- Recover
- People
- Devices
- Data
- Cloud
- Applications
Protection is a coordinated system, not a product. Spicsoft layers perimeter, network, endpoint and email defenses, watches them continuously, and keeps isolated backups so an incident is contained—and recoverable.
Problems this solves
- An antivirus and hope
- No one watching alerts at night
- Cyber-insurance questionnaires you cannot answer
Everything needed to run it—not just install it.
From assessment to ongoing management.
- 1
We assess exposure across your environment.
- 2
We close gaps in layers—perimeter, network, endpoint, identity.
- 3
We monitor continuously and respond as part of your managed service.
- 4
We verify recovery so an incident never becomes a loss.
From assessment to always-on, in six phases.
How Spicsoft delivers Cybersecurity & Ransomware Protection for a business like yours.
- 1Week 1
Assess
Where you are exposed today: perimeter, network, identities, endpoints, email, backups and vendor access. We show you the findings in plain language, ranked by what an attacker would actually try first.
- External & internal exposure review
- Identity and access audit
- Ranked findings, plain language
- 2Weeks 2–3
Harden
Close the easy paths in: MFA everywhere, legacy protocols off, firewall rules reviewed, network segmented, admin rights reduced, patch gaps closed.
- MFA & conditional access
- Firewall & segmentation
- Patch and privilege clean-up
- 3Weeks 3–4
Protect
Behavior-based endpoint protection on every device and server, email filtering against phishing and malware, and a short awareness session so people recognize what the tools cannot catch.
- Endpoint & ransomware defense
- Email security
- Staff awareness session
- 4Week 5
Detect
Every endpoint, identity and firewall now reports to 24/7 monitoring. Alerts are triaged by engineers around the clock, and containment actions are pre-approved with you.
- 24/7 detection & response live
- Alert playbooks agreed
- Containment authority
- 5Week 6
Recover
Isolated, immutable backups verified and restore-tested; an incident plan rehearsed with your leadership: who calls whom, what is isolated first, how the business communicates.
- Isolated backup + restore test
- Incident response plan
- Tabletop rehearsal
- 6Ongoing
Operate
Monitoring, patching, access reviews and awareness continue under one agreement—with quarterly reviews, insurance and audit evidence on request, and the same team on the line if something happens.
- Quarterly security review
- Insurance & audit evidence
- 24/7 response
What changes for your business.
Managed under one agreement with 24/7 monitoring, support and a named team accountable for the result.
- Threats stopped at the layer they arrive at
- Clear visibility into what is protected and how
- Confidence that the business can recover
Straight answers.
Specific to this service. Support hours, onboarding, pricing and service area are covered on our FAQ page.
What happens if ransomware gets in?
Containment at the endpoint, isolation of affected systems, and recovery from isolated backups—following a plan we have rehearsed with you.
Is this only for large companies?
No. The layers scale down; a 20-person practice gets the same model, sized appropriately.
Is antivirus enough?
No. Modern attacks use stolen passwords and legitimate tools, not just malicious files. Behavior-based endpoint detection, MFA, email security and monitoring together catch what antivirus alone misses.
Do you monitor for threats around the clock?
Yes. Endpoint, identity and email alerts are watched 24/7, and a confirmed threat is contained immediately—an infected laptop is isolated at 2 a.m., not at 9 a.m.
Will security slow our staff down?
It shouldn't. Controls are tuned to your workflows, MFA is set up to prompt rarely on trusted devices, and staff are given short, practical training so security becomes routine rather than an obstacle.
Do you provide security awareness training?
Yes. Short, regular sessions and simulated phishing help staff recognise the attempts that get past the filters, with results you can show an insurer or auditor.